-
The hacking group ShinyHunters took control of the leak site of their competitor, the ransomware group cl0P.
-
The attack was due to issues about the theft of an Oracle E-Business Suite Vulnerability exploited for breaking into over hundred firms maliciously.
-
Security experts confirmed the confrontation, noting that capturing server access could bring internal gang communications plus operational data to light.
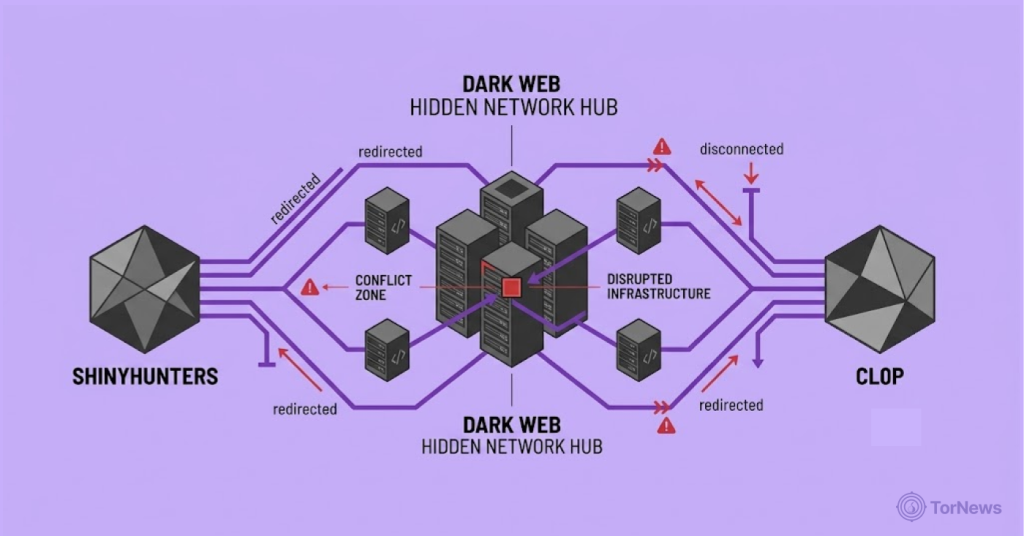
A public fight between popular cybercrime networks has erupted after a top extortion group attacked its main competitor. ShinyHunters, a tough cookie in digital extortion, took control of the dark web site belonging to rival ransomware operation cl0p.
Analysts in cybersecurity intelligence confirmed that the leak platform where the rival gang cl0p posts about their online victims became completely unavailable after the targeted attack.
Dark Web Site Takeover from Technical Exploitation
ShinyHunters compromised the backend servers of cl0p after it found an unpatched software weakness within its internal digital infrastructure. Using this finding, the attackers took administrative control over the hosting environment & operational databases belonging to cl0p.
Due to the takeover, visitors who wanted to open the leak platform of cl0p could not. Instead, they saw a custom defacement notice that the intruders posted directly.
Research platforms that track illicit online platforms got verified screenshots of messages which showed that the rival gang had taken over the site before the portal went offline completely. Furthermore, experts in cybersecurity noted that taking over the infrastructure belonging to a rival network represents a heavy blow to the operations of the victim.
With administrative access in their hands, the threat actors can inspect logs of victim negotiations, private decryption keys, & internal chat communications that were supposed to be confidential. Therefore, this breach has put the reputation of cl0p in jeopardy & opens up sensitive operational details to intelligence monitors all over the world.
Stolen Oracle Zero-Day Vulnerability Dispute Behind Long-Simmering Cybercrime Conflict
The key reason for the opposing mindsets is the long-term problem between these two gangs. The reason was an essential software hack targeting the Oracle E-Business Suite system. The ShinyHunters group mentioned they were the first to discover the exploit, which enabled unauthorized access until the software developers sent emergency updates.
However, the ShinyHunters have accused cl0p of stealing the software code, & then implementing it in many networks worldwide. By utilizing the zero-day flaw, cl0p obtained access to a large number (over 100) of corporate networks.
The same Oracle zero-day was also linked to a breach of security company Entrust, highlighting how the vulnerability was used against high-profile organizations beyond the current dispute between the two groups. As the conflict got hotter, cl0p made a threat that they would reveal the identities of top people at the ShinyHunters group to the public.
In response to that, ShinyHunters warned that it would share internal operational records showing the underlying business operations of cl0p. This means ShinyHunters has weaponized its technical research against the web servers of cl0p, turning threats into a full infrastructure takeover.
High-Profile Extortion Campaigns Highlight Massive Enterprise Software Vulnerability Risks
Both networks of criminals are popular for a lot of high-impact data theft attempts focusing on large organizations of the world. Particularly, the Russian-speaking group cl0p became popular for using zero-day vulnerabilities in some enterprise file transfer systems like MOVEit.
In just that single campaign, the group collected personal records belonging to tens of millions of individuals in almost 600 companies. Recently, cl0p even agreed to have extracted proprietary files from nearly 50 global corporations, including Philips & Shell.
Similarly, ShinyHunters continues carrying out high-profile cyber extortion campaigns against well-known consumer brands, educational institutions, and entertainment developers.
Additionally, security researchers from major artificial intelligence companies recently detected ShinyHunters-linked actors attempting to abuse automated tools for intrusion tasks. The ongoing clash demonstrates how rogue threat actors actively repurpose advanced vulnerability research tools against rival criminal groups.
Industry Security Experts’ Reaction and Broader Threat Landscape Implications
According to analysts in the field of cybersecurity, public clashes between long-established organizations that engage in illegal web activities are rare in the world of cybercrime. Also, experts in threat intelligence note that although conflicts do exist, they seldom result in public cyber warfare against infrastructure.
Moreover, senior researchers tracking underground forums described the direct server invasion as an uncommon operational twist. While experts in cybersecurity constantly keep an eye on dark web forums, cybercriminals often resolve their conflicts on an internal basis, ensuring that law enforcement agencies do not interfere.
Consequently, this public disruption may generate valuable threat intelligence for corporate defense teams and international law enforcement agencies. The intercepted data leaks may expose crucial details on the infrastructure, allowing security teams to permanently bring the extortion efforts to an end. In the long run, fierce conflicts between rival extortion organizations reflect the unstable and unpredictable aspects of the current cybercrime world.
