-
The FBI says cybercriminals are changing their methods as new AI tools open the door to smarter attacks.
-
Brett Leatherman of FBI Cyber and John Fokker of Trellix shared the warning on the FBI’s Ahead of the Threat podcast.
-
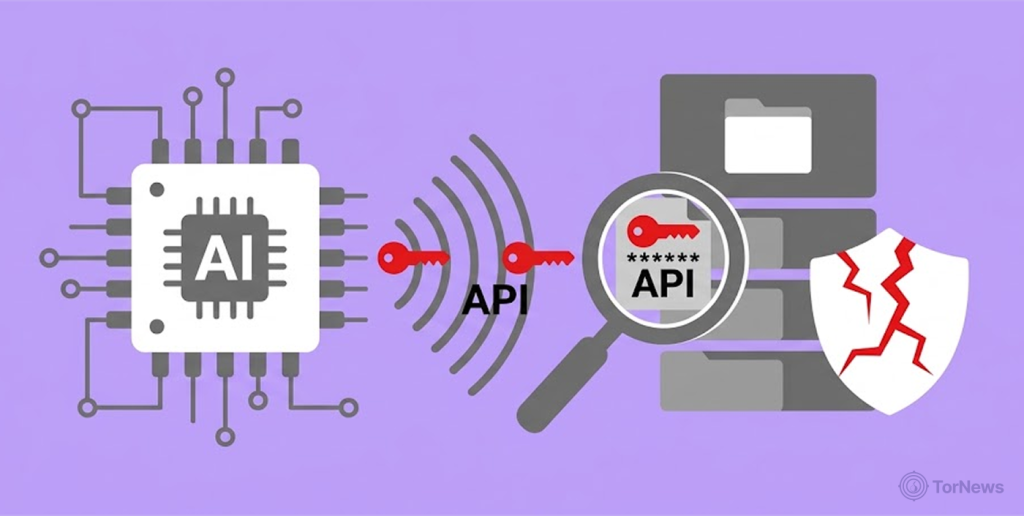
Fokker says AI agents could dig through company knowledge bases for passwords and keys, so defenders should scan first.
The FBI has warned that cybercriminals are changing their methods. New artificial intelligence abilities give them fresh ways to launch smarter attacks. The warning came in the latest episode of Ahead of the Threat, the FBI’s cybersecurity podcast.
Brett Leatherman, Operations Director and head of FBI Cyber, spoke on the show. John Fokker, Vice President of Threat Intelligence Strategy at Trellix, joined him. The FBI published Season 3, Episode 1 on October 29, 2026. People can also listen to the audio version.
The talk covered the changing ransomware scene and the use of super intelligence (SI) in cyberattacks. It also showed how groups can turn threat intelligence into practical security steps. Both guests stressed teamwork between law enforcement and private cybersecurity companies.
Ransomware Gangs Split Into Smaller Crews After Police Disruptions
According to the FBI, cybercriminal groups are becoming more fragmented after law enforcement disruptions. Fokker explained that some larger ransomware groups have broken into smaller operations.
He said investigations and infrastructure takedowns can expose links between criminal operators. He noted that taking down shared infrastructure gives investigators useful information. That information helps them identify other people involved in cybercrime.
A major point of the talk was moving beyond simply collecting and sharing cybersecurity reports. Leatherman said threat intelligence gains value when companies and their security partners act on it. They can use it to find harmful infrastructure, recognise suspicious activity, and stop new threats. The FBI also keeps a cyber strategy page on its website.
Fokker agreed with this view. He explained that security companies hold wide knowledge about attacks. They gain it through their security products and customer environments. This view can support investigations. Companies must share the relevant intelligence through proper legal and operational channels. Trellix also lists a 2026 threat hunting report on its website.
Leatherman and Fokker agreed that strong cyber defence needs closer cooperation. Businesses, security vendors, and law enforcement agencies must work together. They discussed the value of industry partnerships and information-sharing groups. They also praised established channels. These let organisations build relationships with investigators before an attack happens.
Super Intelligence May Help Attackers Hunt for Hidden Passwords
The panel also looked at how SI could help attackers. Fokker said it could make finding exposed credentials, vulnerabilities, and sensitive information easier. This data can hide across corporate systems. He used platforms such as Jira and Confluence as examples.
Attackers could send AI-powered agents into large internal knowledge bases. These agents could search for passwords, API keys, and other valuable details. Fokker said this works much faster than manual methods.
He urged defenders to adopt similar tools. They can scan their own environments nonstop. They can find exposed information and fix security weaknesses before criminals exploit them. Businesses are also exploring AI agents for threat monitoring, with Google deploying Gemini AI agents to monitor dark web threats for businesses.
Leatherman also stressed that basic weaknesses remain a major way in for attackers. Unpatched software can still expose organisations. So can outdated user accounts, stolen credentials, and poorly managed IT assets. This holds true even as attack methods become more advanced.
The episode reinforces the FBI’s position that intelligence sharing should lead to action. Exchanging reports and technical indicators is not enough. Attackers are adopting faster and more automated techniques. Organisations must therefore improve how they detect unusual activity, protect sensitive information, and respond quickly.
X Users Doubt Police Results While Others Share Defense Ideas
The FBI’s announcement drew criticism and suggestions from users on X. Several questioned whether law enforcement efforts lead to meaningful action against cybercriminals.
Clarence Stewart, posting as @clarenc90624486, criticised what he described as weak accountability. He argued that authorities sometimes identify criminals without making arrests or enforcing consequences. Another user, @AnnieM2022, voiced similar frustration. The user claimed that agencies can ignore reports even after people submit evidence.
These comments are individual opinions and allegations. They are not verified evidence of how the FBI handles cybercrime complaints.
Other replies focused on practical steps. @Insider747, posting as Digital Life, recommended starting with a zero-trust security environment. The user also suggested using autonomous AI research to find and block possible attack paths before criminals use them. CISA publishes a zero-trust maturity model for readers who want to learn more.
Meanwhile, @jandicehumpry argued that some successful incidents come from poor IT management, not clever hacking. In the user’s words, it hardly counts as a hack when the IT team lacks skill.
