-
A crypto tracking app called FomoPeek hid harmful code that could break into iPhone security and grab private data.
-
Security researchers from SlowMist and OKX say hackers used the app to steal close to $580,000 in crypto.
-
The app removed the harmful code in a later update, but experts still warn anyone who used the earlier versions.
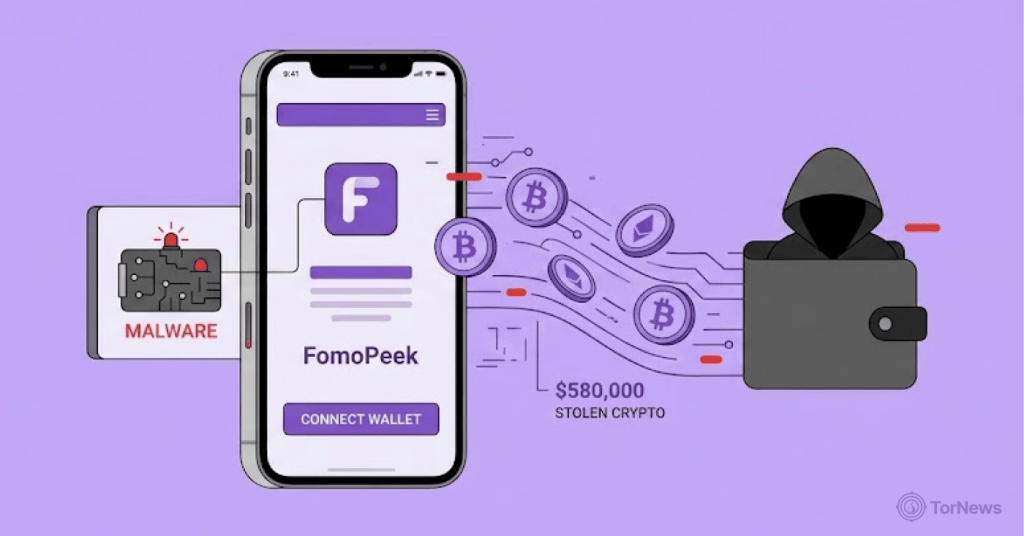
An app on Apple’s App Store promised to track crypto wallets safely. Instead, it carried hidden code built to break into iPhone defenses. Blockchain security firm SlowMist and the OKX security team uncovered the scheme after several users reported stolen funds.
The app, FomoPeek, claimed to only watch wallets from a distance. Its App Store page said (that’s now deleted by Apple) it never connected to a user’s wallet, made trades, or held funds. WhaleScanv built the app, and Porter Manufacturing, L.L.C. listed it as the seller. That promise turned out to hide something far more dangerous.
Hidden Code Found Inside the App
SlowMist began digging after users said they lost crypto after installing FomoPeek. Investigators traced the losses to two versions of the app, 1.1 and 1.2. Both versions carried code that had nothing to do with wallet tracking.
One hidden module held a kernel exploit toolkit built for iPhones. It came packed with eight different attack methods. The app could pick a method based on the phone model and its iOS version.
If the attack worked, FomoPeek could break out of Apple’s normal app restrictions. Windows users have faced similar concerns involving vulnerabilities that can give attackers elevated privileges. A dark web seller claims $100,000 Windows 11 zero-day elevates users to SYSTEM covers an alleged Windows 11 zero-day that could allow attackers to gain SYSTEM-level access. It could then read protected data stored in the phone’s Keychain. That data often includes passwords, login details, and saved credentials.
The code could also open files that belonged to other apps on the phone. Investigators found a list of 19 target apps, including several crypto wallets. Apple Notes also made the list, a detail that matters because people often save recovery phrases there.
The hidden module talked to secret servers that had nothing to do with FomoPeek’s real service. Those servers could send commands to the app from far away. Researchers who studied the app’s network traffic said the attack could run on its own at set times, without any action from the user.
A closer look at older versions showed the harmful code was not there from the start. Version 1.0 came out clean. Version 1.1 added the hidden modules on September 9. Version 1.2 kept them when it launched on September 12. Version 1.3, released on September 17, finally removed both modules.
Attackers Stole Nearly $580,000 in Crypto
SlowMist tracked the stolen funds across several blockchains. Investigators say one main wallet address collected close to 579,984 USDT, worth nearly $580,000. From there, the funds moved through a chain of other wallets and services, a pattern investigators say hides the trail of stolen money.
A blog post from Safeheron walked through how the theft likely unfolded, step by step. The attackers appear to have targeted people who trusted the app’s promise of safe, read-only tracking. That trust is exactly what let the hidden code slip past notice for weeks.
News outlets picked up the story soon after SlowMist shared its findings. Cointelegraph and Crypto Times both reported on the joint investigation by SlowMist and OKX. Both outlets confirmed the same core details about the exploit and the stolen funds.
The case shows how an app can look harmless on the surface while hiding a much bigger threat underneath. FomoPeek passed Apple’s review process and reached real users before anyone caught the problem.
SlowMist Tells Users How to Stay Safe
SlowMist shared clear steps for anyone who installed FomoPeek versions 1.1 or 1.2. Users should check their crypto accounts right away for any activity they don’t recognize.
Anyone affected should set up a brand new wallet and recovery phrase. This should happen on a separate device that never had the app installed. Users should then move any remaining crypto to that new wallet as soon as possible.
SlowMist also told users to update their iPhone software right away. Keeping iOS current closes off some of the paths the hidden code could exploit. Users should avoid reinstalling FomoPeek altogether, even the newer, cleaned-up version.
This incident stands as a reminder that an app store listing alone can’t guarantee safety. A tool built to protect your crypto can just as easily become the thing that puts it at risk. Staying alert, and acting fast when something feels wrong remains the best defense.
